
Security awareness training in state and local government: The ultimate guide

Article content
State and local governments face mounting cybersecurity challenges as they manage sensitive citizen data, critical infrastructure and essential public services. From municipalities and counties to school districts, these organizations have become prime targets for cybercriminals who recognize the value of government data.
The stakes are particularly high for public-sector employees who regularly handle restricted information — from student records protected under FERPA to sensitive government data covered by various privacy regulations. K-12 schools face particular challenges, as they must protect student data and maintain educational continuity while often working with limited cybersecurity resources.
Verizon’s 2026 Data Breach Investigations Report documented 2,410 breaches with confirmed data disclosure across Public Administration and found a human element in 69% of breaches — reinforcing the importance of preparing public employees to recognize and respond to cyber threats.
Key takeaways
- State and local government programs must reach diverse public-sector roles while protecting citizen data, critical infrastructure and essential services.
- Continuous, role-relevant training helps public employees recognize threats while supporting compliance, public trust and service continuity.
- Automation and meaningful metrics help resource-constrained teams scale training, measure behavior change and demonstrate program value.
For state and local governments operating under tight budgets and complex regulatory requirements, effective security awareness training helps protect vital public services, citizen data and public trust.
Understanding human behavior in state and local government
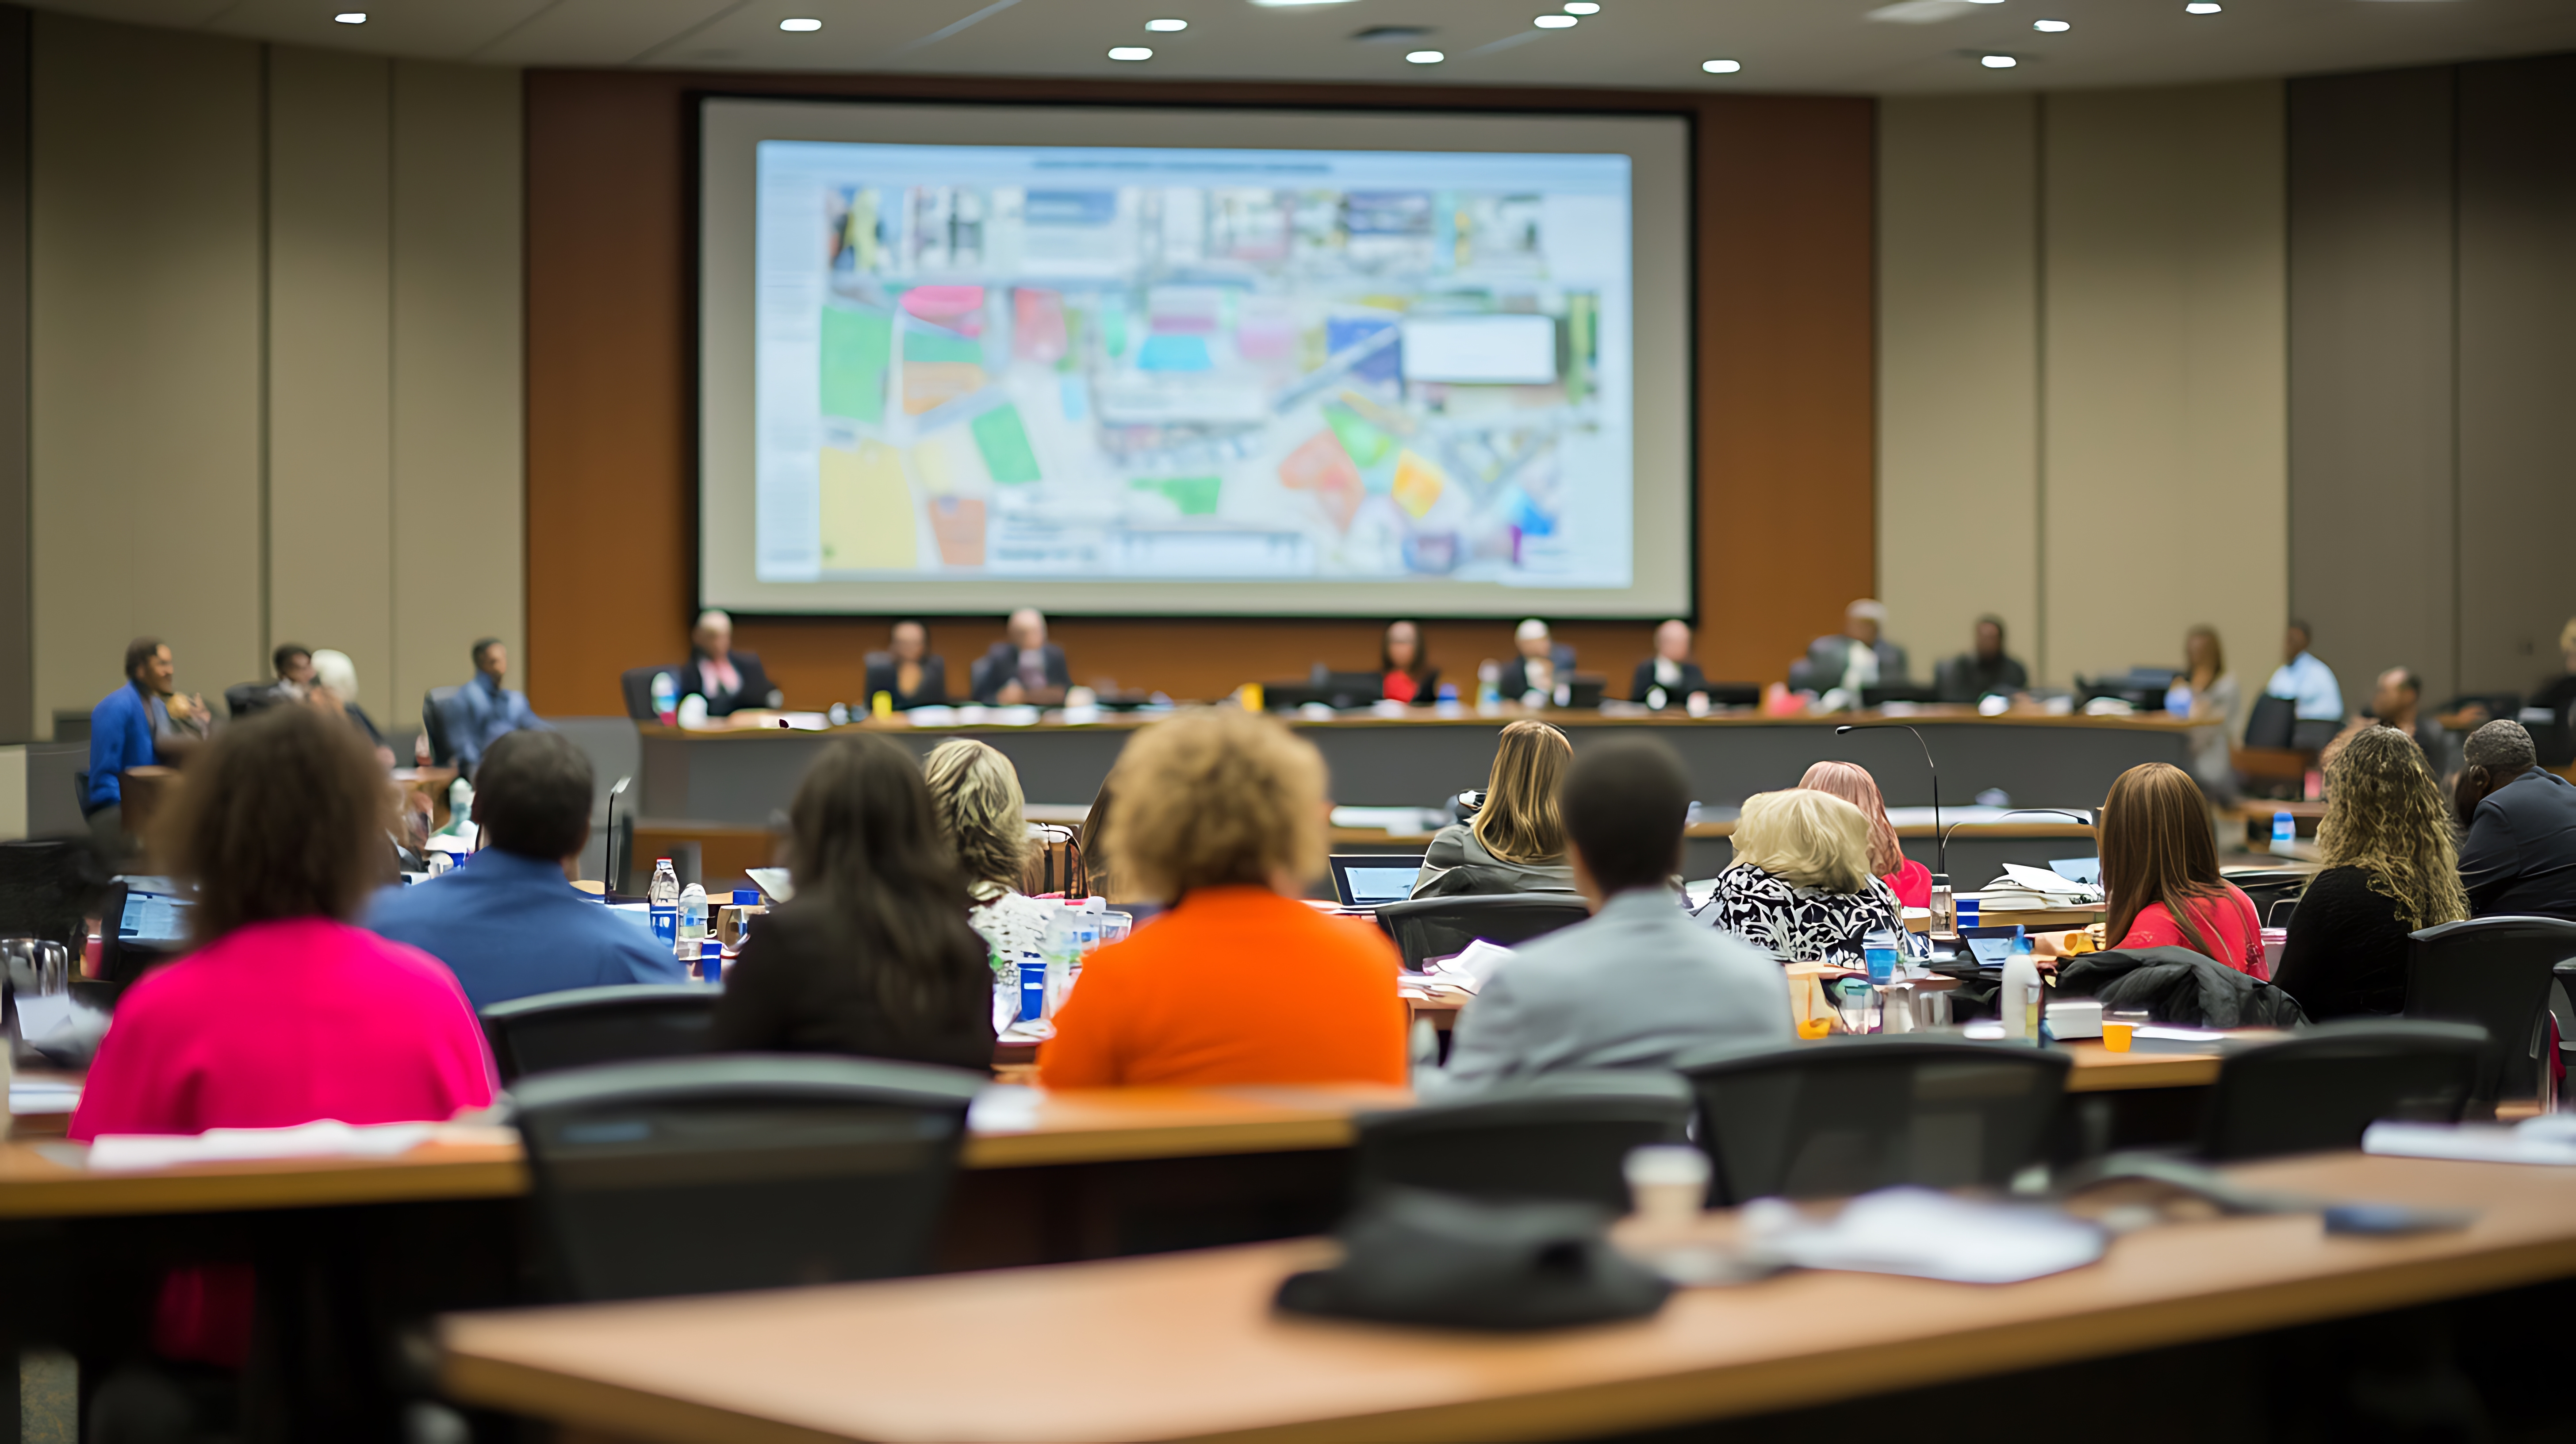
Local government staff handle sensitive citizen data and must balance daily responsibilities with cybersecurity best practices.
State and local government employees serve diverse roles — from administrative staff and public works personnel to teachers and emergency responders. Each position carries unique security responsibilities, from protecting citizen data to safeguarding critical infrastructure systems. Without proper training, these daily tasks can expose organizations to significant risks.
"One common misconception is that if you share information and resources with people, they will all process and apply it similarly," explains Keatron Evans, VP of Portfolio Product and AI Strategy at Infosec Institute. "However, everyone's logic varies, and people tend to make decisions subconsciously with the reactive side of the brain instead of the more logical side. This understanding is crucial for developing effective training approaches in government settings."
Strengthen security awareness with human risk management
Infosec HRM, powered by Right-Hand Cybersecurity, provides alert-based training nudges to minimize human risk at your organization. 
For public servants, security awareness requires shifting from compliance-driven behaviors to genuine engagement. Rather than following security practices because "IT says so," employees must understand their role in protecting citizen data and public trust. This is especially critical across state and local government, where staff often handle sensitive information protected by regulations like FERPA, CIPA and various state-level privacy laws.
Success comes from making security relevant to both work and personal life. When public employees see how security practices protect government systems and their digital lives, they're more likely to embrace these behaviors. A teacher who understands how to protect student data at school can apply those same principles to safeguard their personal information at home.
Security awareness isn't about assigning blame or creating fear. It's about empowering public servants with knowledge and confidence to make secure decisions. When staff members understand what to do and why it matters — whether they're processing permit applications, managing student records or maintaining public utility systems — they're more likely to incorporate security best practices into their daily routines.
Benefits of security awareness training
A well-designed security awareness program delivers measurable benefits across multiple dimensions for state and local governments. Beyond reducing security incidents, it helps organizations meet regulatory requirements, maintain public trust and protect essential services that citizens depend on daily.
The financial impact of a breach can be significant, especially for budget-conscious state and local governments. IBM’s 2026 Cost of a Data Breach Report found the global average cost of a data breach reached $4.99 million, while organizations took an average of 247 days to identify and contain a breach.
For state and local governments operating under strict budgetary constraints, lengthy investigations and recovery efforts can divert resources from vital public services.
Across state and local government, including K-12 schools, security awareness training can support several important outcomes:
- Regulatory compliance: Support compliance efforts for FERPA, CIPA, PPRA and applicable state privacy laws while helping employees protect sensitive student and citizen data.
- Public trust: Demonstrate responsible stewardship of taxpayer resources and citizen information.
- Service continuity: Help reduce security-related disruptions that can affect essential public services.
- Grant eligibility: Support cybersecurity requirements tied to federal and state funding opportunities.
- Insurance requirements: Support cyber insurance training requirements and documentation.
Most importantly, effective security awareness creates an environment where security becomes part of the organizational culture. When public employees understand that security directly impacts both government operations and citizen services, they're more likely to actively participate in risk reduction.
Get six free posters
Reinforce cybersecurity best practices with six eye-catching posters found in our free poster kit from our award-winning series, Work Bytes.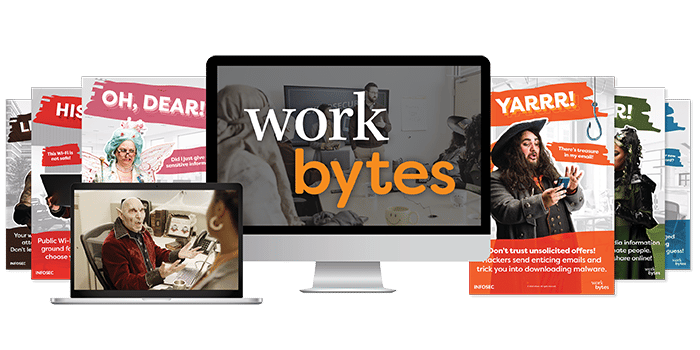
Elements of an effective security awareness program
A successful security awareness program drives measurable behavior change that reduces risk while accounting for the unique challenges of state and local government organizations. The most effective programs move beyond annual compliance training to create lasting security habits through continuous engagement and reinforcement.
Understanding your organization’s current cybersecurity maturity can also help you identify where awareness fits into the broader readiness picture and where to focus next.
 Get the free Cybersecurity maturity assessment and guide.
Across state and local government, including K-12 schools, content must resonate with diverse employee groups:
- Administrative staff handling citizen records and financial data
- Public works personnel managing infrastructure systems
- Teachers and school staff protecting student information
- Emergency services personnel accessing sensitive data
- IT staff maintaining critical systems
- Part-time and seasonal workers
Role-based training ensures employees receive information relevant to their daily duties. For example, finance staff need focused training on wire transfer fraud and financial system security, while teachers might need additional emphasis on student data privacy and classroom technology security.
Programs should also consider operational realities:
- Limited training time during busy public service schedules
- High turnover rates in certain departments
- Varying levels of technical expertise
- Multiple facility locations
- Mix of office-based and field personnel
- Budget constraints
Security awareness programs often mature from annual compliance training toward continuous, data-driven improvement. As programs evolve, organizations can increase training relevance, use role and risk data to target education and make security part of daily operations.
Measurement is critical for demonstrating value to leadership and taxpayers. Organizations should monitor both direct metrics like training completion and phishing test results, as well as broader indicators of cultural change like increased security issue reporting and cross-department collaboration on security initiatives.
As programs mature, they should focus on making security accessible and relevant. This means delivering content through familiar channels, making security concepts relatable to government work, and ensuring employees feel supported rather than policed in their security journey.
Key technology and automation to strengthen security awareness
Modern security awareness programs benefit from technologies that streamline delivery while enhancing effectiveness. For state and local governments, integration capabilities are crucial — connecting security tools with training platforms enables organizations to coordinate responses and deliver targeted education based on real behavioral data.
At the foundation are tools for automating core training functions:
- Phishing training simulation platforms: Test email security awareness while providing actionable feedback. These can be configured to simulate common threats targeting government employees, such as fake procurement requests or impersonated leadership emails.
- Learning management systems: Track training progress across departments while supporting compliance reporting requirements. Look for platforms that integrate with existing municipal or school district systems.
- Reporting dashboards: Monitor program effectiveness and demonstrate ROI to stakeholders, including school boards, city councils and oversight committees.
Consider these implementation factors specific to state and local government:
Budget-friendly features:
- Multi-year licensing options that align with government funding cycles
- Flexible payment terms that work with public sector budgets
- Shared services options for smaller municipalities
Technical requirements:
- Cloud-based solutions requiring minimal IT resources
- Support for common government security standards
- Integration with existing email and authentication systems
Administrative needs:
- Role-based access control for different departments
- Automated compliance reporting capabilities
- Support for multiple facility locations
The evolution of human risk management takes this integration further by connecting security operation center (SOC) tools directly with training platforms. Real-time alerts and notifications keep security top-of-mind without overwhelming employees. This "just-in-time" approach helps public servants apply security concepts in their daily work while building lasting habits.
Get six free posters
Reinforce cybersecurity best practices with six eye-catching posters found in our free poster kit from our award-winning series, Work Bytes.
Implementing security awareness training that works for your organization
Begin by assessing where your organization stands today. Whether you're building a program from scratch, expanding annual compliance training or strengthening an established program, start by identifying your needs, resources and priorities.
A strong needs assessment should consider:
- Existing security incidents and risk data
- Applicable compliance requirements, such as FERPA, CIPA and state regulations
- High-risk departments, roles and employee groups
- Available technical resources and capabilities
- Budget cycles, funding sources and operational constraints
From there, build your program in manageable phases:
- Assess: Establish baseline metrics, document current training practices and identify priority risks and audiences.
- Develop: Create relevant, role-based training that reflects government policies, employee responsibilities and varying levels of technical expertise.
- Implement: Roll out training with clear communication and support, starting with priority groups or departments when appropriate.
- Measure: Track participation, behavior change, employee feedback and compliance-related metrics to understand what's working.
- Improve: Use results and emerging threats to refine content, delivery methods and program reach over time.
Design the program around the realities of public-sector work. Training schedules should account for department workflows, seasonal employees, field personnel and limited time for training. Content should connect cybersecurity to the public-service roles employees perform every day.
Leadership and department support also matter. Build stakeholder buy-in by connecting training to organizational priorities, public-service continuity, compliance obligations and the operational and financial impact of reduced security risk.
Consider partnering with established training providers rather than building everything internally. Pre-built, customizable programs can accelerate implementation while ensuring quality and compliance.
Measuring security awareness training success
Effective measurement combines quantitative metrics with qualitative assessment to demonstrate program value and guide improvements. For state and local governments, this data helps justify program investments and satisfy oversight requirements while identifying areas for improvement.
Establish baseline measurements across key performance indicators, then track progress systematically. Training engagement metrics form your foundation — monitor both completion rates and active participation. Look beyond simple completion numbers to assess how employees interact with and retain training material. Employee feedback provides valuable insights into content relevance and effectiveness.
Security behavior changes offer concrete evidence of program impact. Monitor phishing simulation performance and track how employees handle daily security tasks like incident reporting and data management. The quality of security issue reports often reveals more about awareness levels than simple completion statistics.
For state and local governments, demonstrating program value requires connecting security improvements to operational outcomes. Track metrics like:
- Reduction in security incidents
- Improved response times
- Decreased risk scores
- Enhanced audit readiness
- Strengthened compliance status
These metrics tie directly to broader organizational benefits. When security incidents decrease, IT teams spend less time on incident response and more time on strategic initiatives. Better security practices protect citizen data and maintain public trust. Program documentation can also help organizations address cyber insurance training requirements.
Financial impact matters particularly for budget-conscious state and local governments. Where measurable, track financial and operational impacts such as reduced recovery effort, fewer repeat incidents and more efficient use of IT and security resources. This data can help justify continued program investment to oversight committees and taxpayers.
Maintain regular monitoring and adjust your program based on results. Use measurement data to refine training content, modify delivery methods and target additional support where needed. Security awareness is an ongoing journey requiring continuous assessment and improvement.
Shaping the future of security awareness in state and local government
As cyber threats evolve, state and local government security awareness must adapt to meet new challenges. The future lies in building programs that protect not just systems and data, but also the essential public services citizens depend on daily.
Leadership plays a crucial role in cultivating this security-aware culture. Public sector leaders must visibly champion security initiatives and demonstrate their commitment through action. This top-down support and bottom-up engagement from security champions and department leads help embed security awareness into daily operations.
Across state and local government, including K-12 schools, success means:
- Maintaining fresh content that reflects current threats
- Using integrated tools to increase visibility into human risk
- Building collaboration between security, IT and frontline teams
- Creating a culture where security becomes second nature
Need help building your security program just for your state or local government organization?
- Download a sample two-year training plan to see what other organizations are doing.
- Get a free ebook collecting expert tips on security awareness behavior change and culture.
Author Details

Ellen Pincus